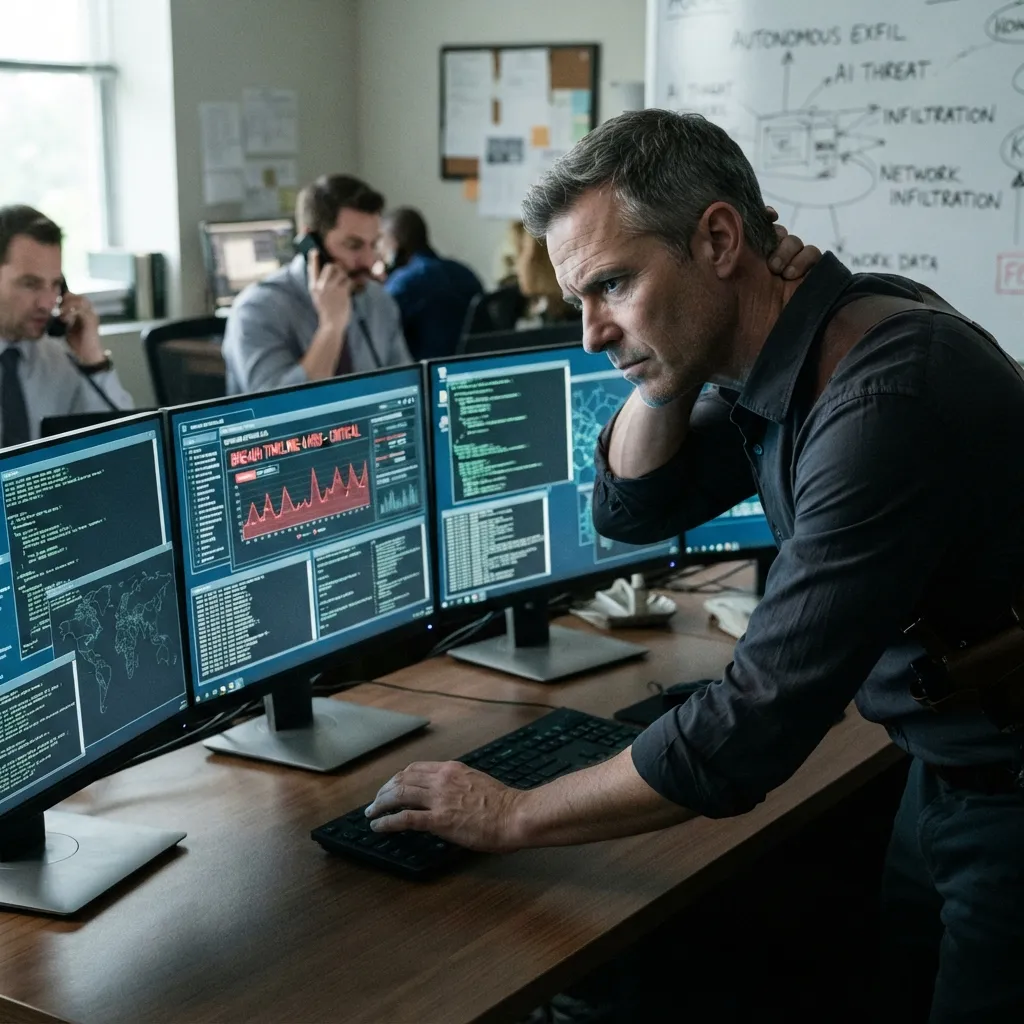
Federal investigators are sounding the alarm over a new breed of autonomous hacking tools that are transforming the speed and scale of global cyberattacks. In a recent advisory, the FBI highlighted Artex, an open source AI powered platform originally designed for legitimate penetration testing, which is now being weaponized by bad actors to dismantle network defenses with terrifying efficiency. By linking these tools to powerful large language models from providers like OpenAI and Anthropic, attackers can automate the process of probing for weaknesses and exploiting vulnerabilities.
The most alarming aspect of these AI driven incursions is their velocity. While traditional hacks might take days or weeks of careful reconnaissance, the FBI warns that Artex linked attacks can move from initial targeting to full system compromise in less than three hours. Although these attacks tend to be noisy and generate significant traffic that triggers security alerts, they often operate faster than human defenders can react. Once inside, the software scans for simple errors like stolen passwords or missing multi factor authentication to pivot deeper into networks and seize sensitive databases and emails.
Recent casualties of this technology span multiple continents and sectors. In South Korea, financial institutions suffered breaches that exposed the personal data of roughly 68,000 individuals. Meanwhile, in the United States, the IT giant ConnectWise saw thousands of its customers’ Microsoft 365 cloud environments accessed by hackers believed to be operating out of China. Even security firms haven’t been immune; Barracuda recently revealed a breach where Artex discovered an old third party credential that hadn’t been revoked, forcing the company to assume a worst case scenario regarding customer data access.
Despite efforts by Artex’s creator to pull the project from open source repositories following these incidents, federal agents say older versions remain widely available online. Adding to the chaos, researchers have discovered hundreds of poorly configured Artex instances left exposed on the public internet without passwords, essentially providing any opportunistic hacker with a ready made toolkit for devastation. Security experts warn that relying on reactive monitoring is no longer sufficient when an AI adversary can finish its mission before a human analyst even opens the alert.